
 Pradipta eManuel
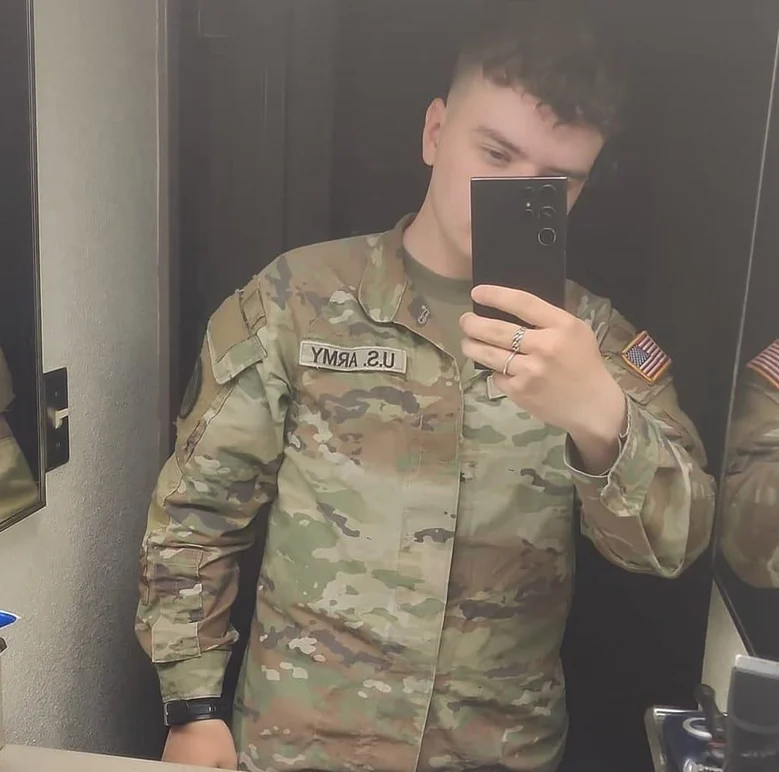
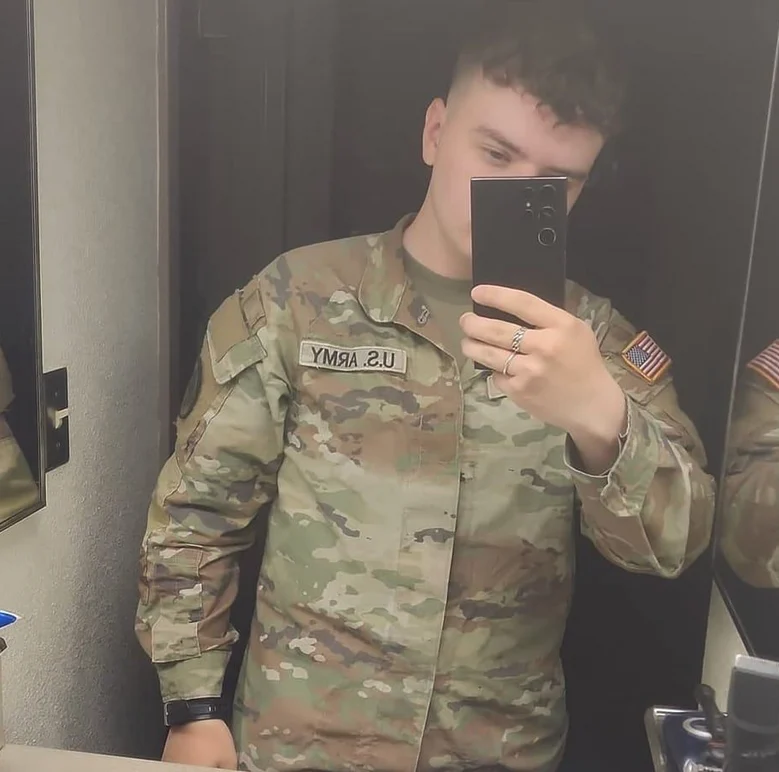
A U.S. Army soldier, Cameron John Wagenius, 22, has been sentenced to 70 months in federal prison and ordered to pay nearly $300,000 in restitution for hacking into telecommunications companies, including AT&T and Verizon, and stealing the mobile call and text metadata of over 100 million customers. Stationed in South Korea at the time of the offenses, Wagenius operated under the cybercriminal alias "Kiberphant0m" and collaborated with at least three other individuals. His illicit activities involved exploiting vulnerabilities in the cloud data storage service Snowflake, which had exposed credentials and lacked mandatory multi-factor authentication at the time, though Snowflake has since rectified this security gap.
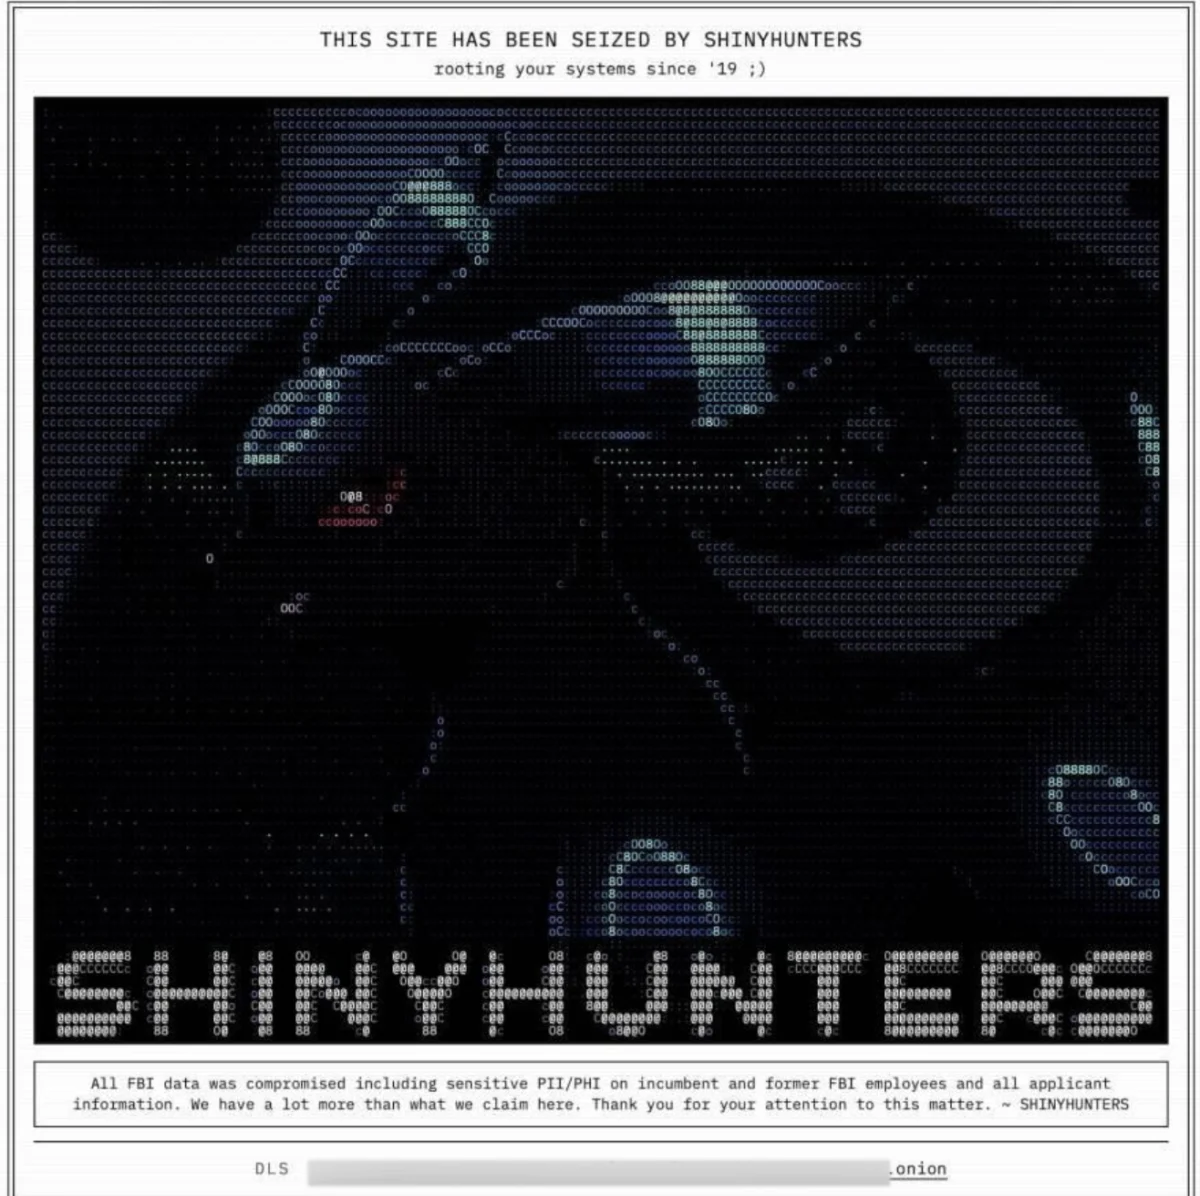
Wagenius’s criminal enterprise came to light in October 2024 when Kiberphant0m boasted on cybercrime forums about obtaining call and text metadata for tens of millions of AT&T customers. He claimed to have compromised over a dozen telecommunications companies globally, including Verizon’s Push-to-Talk business, and engaged in extortion by threatening to release the stolen data. This online bravado eventually led to an investigation by KrebsOnSecurity, which in November 2024 published an article suggesting Kiberphant0m was likely a U.S. soldier in South Korea. This warning proved prescient, as Wagenius was arrested less than a month later and subsequently pleaded guilty to charges in two separate federal indictments.
During his sentencing hearing in Seattle, it was revealed that Wagenius was not acting alone. Federal prosecutors highlighted the involvement of Kenneth Schuchman, a 28-year-old from Vancouver, Washington, with a significant cybercriminal past, including a 2019 guilty plea for operating the Satori botnet. Two other alleged co-conspirators, Conor Riley Moucka, also known as "Judische," from Ontario, Canada, and John Erin Binns, an American residing in Turkey, are also facing charges. Moucka pleaded guilty in August 2026 in connection with the Snowflake data thefts, while Binns is also sought for his alleged role in a massive 2021 data breach at T-Mobile that exposed the personal information of at least 76 million customers.
The scope of Kiberphant0m’s criminal actions extended beyond data theft and extortion. He admitted to re-extorting victims and making threats to disclose national security secrets. Following Moucka’s arrest, and after AT&T had already paid a $370,000 Bitcoin ransom, Kiberphant0m posted purported call logs of then President-elect Donald Trump and then Vice President Kamala Harris, as well as alleged schematics stolen from the U.S. National Security Agency (NSA), on hacker forums.
The investigation into Wagenius’s activities was a multi-agency effort, spearheaded by the Defense Criminal Investigative Service (DCIS), the investigative arm of the U.S. Department of Defense Office of Inspector General. Paul Russell, a resident agent in charge at DCIS, noted the unusual nature of the case, stating, "We don’t often get leads where there’s an active duty soldier with a secret clearance who’s creating hacking tools and trafficking in data. That doesn’t happen every day, and so when that hits it really spins all of our partner organizations up. It was very serious from jump street, just because it was unique, it was an insider threat, and we weren’t sure what we were dealing with." The FBI, the Army Criminal Investigative Division (CID), and the U.S. Secret Service also collaborated on the investigation.
Despite his cooperation and early guilty plea, Wagenius’s post-arrest behavior revealed a continued interest in cyber vulnerabilities. A sentencing memo filed by federal prosecutors in Seattle detailed instances where Wagenius, while incarcerated and awaiting sentencing, attempted to probe the computer network of the Bureau of Prisons (BOP). In September 2025, he used another inmate’s email to ask an AI tool about Windows 10 Enterprise privilege escalation vulnerabilities and exploit scripts. Less than a week later, he used a different inmate’s email to request detailed steps and code for CVE-2023-45208, a command injection vulnerability in D-Link networking devices. He also inquired about constructing an antenna in a prison environment to improve radio reception and, astonishingly, asked for research on escaping prison.
Wagenius often framed these AI queries as being related to a book he was writing, a tactic described in the memo as "prompt injection," where deceptive inputs are fed into AI tools to circumvent security measures. While the government stated there was no evidence Wagenius successfully exploited BOP systems, he claimed his research was intended to provide information to the BOP.
Remarkably, despite the immense potential value of the data stolen from AT&T and other telecom providers, Wagenius’s extortion efforts were not financially lucrative. The government’s sentencing memo indicated he made approximately $1,500 from selling stolen data. However, the memo emphasized that while his financial success as a cybercriminal was limited, his actions demonstrated an intent to cause and did cause significant harm to numerous individuals, U.S. companies, and the U.S. government. The 70-month prison sentence and substantial restitution order underscore the severity of his crimes and the ongoing threat posed by insider threats in the digital realm.