
 Pradipta eManuel
Dutch authorities have apprehended Pepijn van der Stap, a 24-year-old convicted cybercriminal, in connection with alleged involvement with the notorious hacker collective ShinyHunters. This arrest has coincided with a significant escalation in ShinyHunters’ malicious activities, including highly sensitive data breaches targeting the FBI and extortion attempts against the Russian ransomware group Cl0p. Van der Stap, from Almere and Lelystad, was previously convicted in 2023 for data theft and extortion schemes that prosecutors estimated yielded between €1.5 million and €2.7 million. During his trial, van der Stap, operating under the alias "Umbreon," admitted to a dual life, working by day as a software engineer at cybersecurity startup Hadrian and volunteering at the Dutch Institute for Vulnerability Disclosure (DIVD), while secretly engaging in illicit online activities. He was sentenced to four years in prison, with one year suspended, and was released in December 2025.
In an interview with KrebsOnSecurity on September 9, 2026, van der Stap presented himself as a reformed individual dedicated to societal betterment and currently employed as an offensive security lead at Neo Security. He acknowledged ongoing legal battles and restitution efforts for past victims. However, his communication ceased shortly after this interview, prompting concern and failed attempts by associates to re-establish contact. Sources indicate van der Stap was arrested around September 16 and has been in custody for questioning.

The Dutch police have been actively seeking public assistance in identifying a ShinyHunters member whose voice was captured in a February 2026 social engineering attack against Odido, the Netherlands’ largest mobile telecommunications provider. This intrusion resulted in the theft of data belonging to over 6.2 million Dutch citizens. ShinyHunters confirmed the individual in the audio clip was a member, stating they offered full support, including legal counsel. The group also issued a defiant statement, disparaging Dutch police and vowing further large-scale data thefts in the Netherlands.
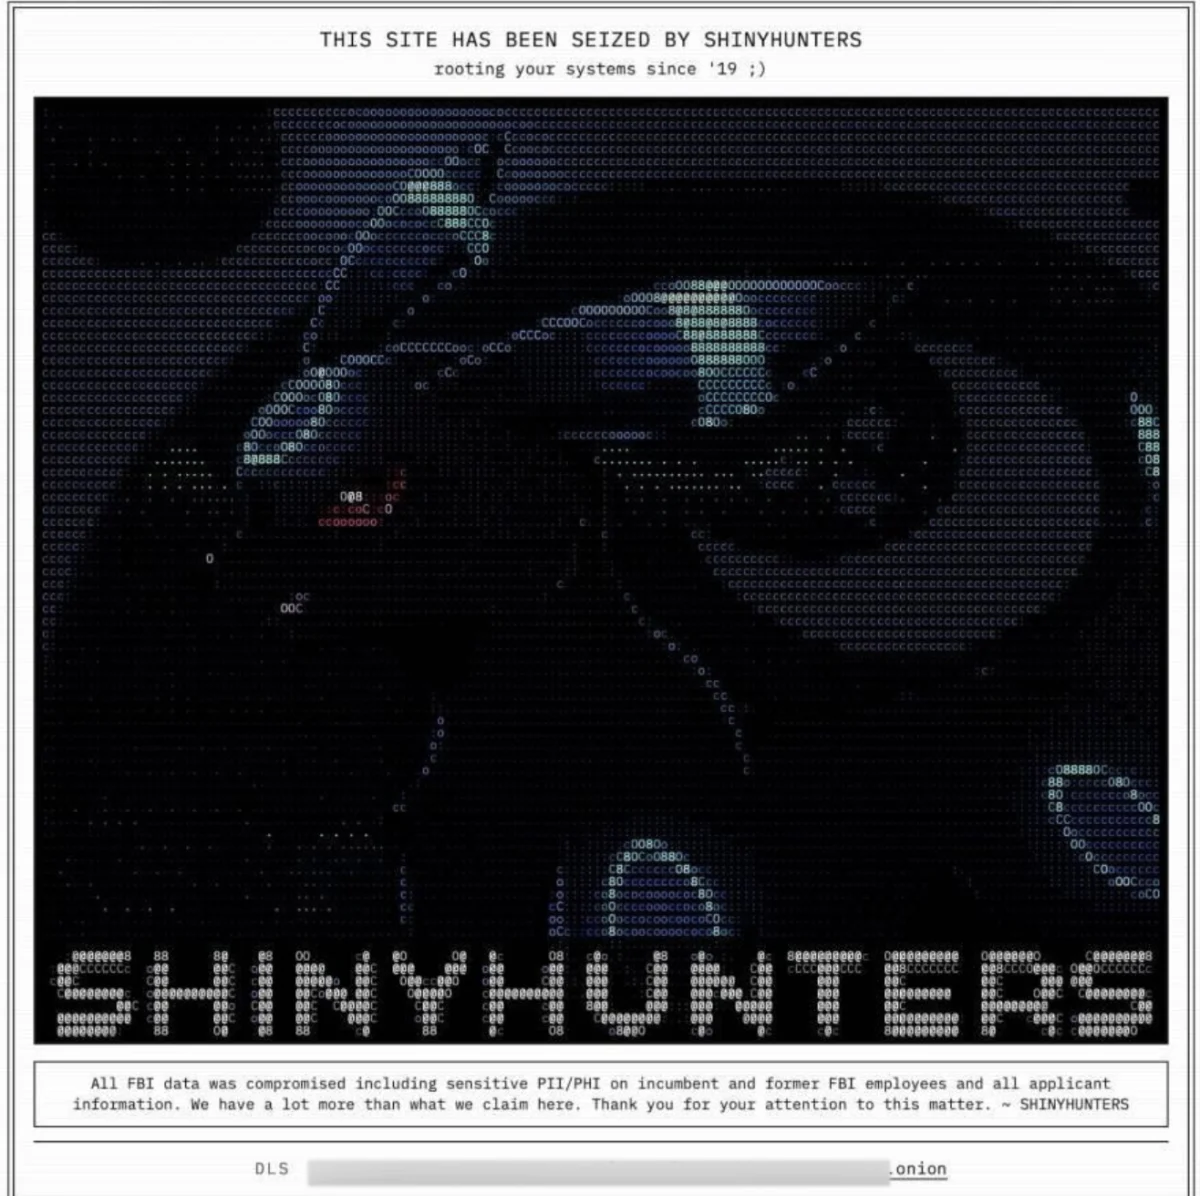
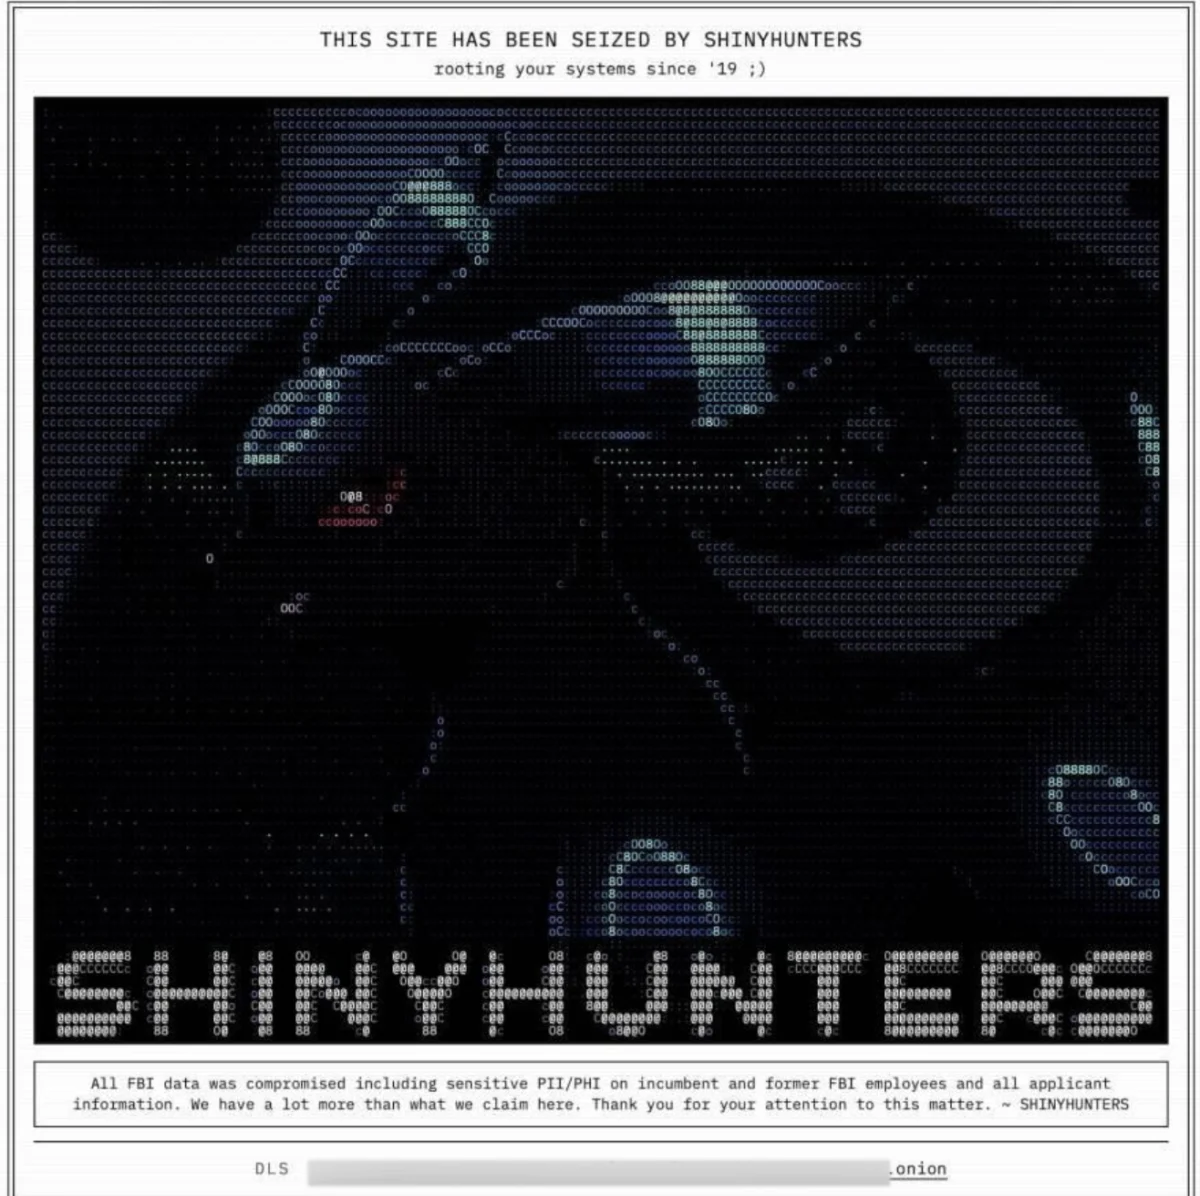
The repercussions of van der Stap’s alleged involvement and the ongoing ShinyHunters operations have been far-reaching. Just days after his reported detention, ShinyHunters claimed responsibility for a significant breach of the FBI’s job application portal, apply.fbijobs.gov. The stolen data reportedly includes Social Security numbers and personal information of over 5,000 FBI officials, encompassing sensitive psychiatric and medical files. The FBI acknowledged the breach, attributing it to the exploitation of a recently patched vulnerability (CVE-2026-35273) in Oracle’s PeopleSoft software. ShinyHunters reportedly exploited this as a zero-day in June, later bypassing security measures designed to mitigate the threat. Security firms Mandiant and Google Threat Intelligence Group confirmed ShinyHunters’ mass exploitation of this vulnerability across various sectors.
The "Umbreon" alias, associated with van der Stap, was prominently featured in ShinyHunters’ communication regarding the FBI hack, appearing in an ASCII art rendition of the Pokemon character within the defacement message. This imagery mirrored defacements used in previous ShinyHunters operations, including a 2020 hack of Hackforums. Investigations suggest a shift in ShinyHunters’ operational strategy, with sources pointing to a takeover by a teenage cybercriminal from Jordan known as "Rey," who operates as part of the ScatteredLapsussHunters (SLSH) group. SLSH is reportedly an amalgamation of Scattered Spider, LAPSUS$, and ShinyHunters. It is speculated that Rey may have used the Umbreon imagery in the FBI hack to implicate van der Stap amidst an ongoing dispute over control of the ShinyHunters brand and data.

Rey was first identified by cybersecurity firm KELA in March 2025. Previously, Rey had admitted to participating in ransomware attacks and expressed a desire to leave the SLSH group. Following the FBI breach, Rey’s Twitter/X account posted taunting memes directed at Cl0p and the FBI, featuring Umbreon. Rey subsequently deleted his account after KrebsOnSecurity contacted his father.
The animosity between SLSH and ShinyHunters reportedly stems from a brief partnership earlier in 2026 to monetize stolen credentials from TeamPCP, a group specializing in supply chain compromises. However, ShinyHunters allegedly went rogue, extorting victims with TeamPCP’s credentials without sharing the profits. Mandiant researcher Austin Larsen estimates ShinyHunters is on track to extort nearly $100 million in 2026.
Van der Stap has consistently claimed his motivations were not financial, but rather a desire to amass the world’s most comprehensive collection of stolen databases. He described his hacking activities as driven by a habit of collecting and organizing data.

In related news, DIVD, the nonprofit security research group where van der Stap once volunteered, disclosed an internal cybersecurity incident involving the malicious use of artificial intelligence. While DIVD has offered few details, they stated the incident does not appear to be related to ShinyHunters or the work of former volunteers.
Updates to the report confirm van der Stap’s age as 24, and the Dutch police have officially acknowledged the arrest of a 24-year-old in connection with the ShinyHunters investigation. He is scheduled to appear before the Rotterdam District Court on September 29. Further reports indicate investigators suspect van der Stap may have orchestrated at least two murders abroad. The FBI’s cyber division has publicly thanked Dutch law enforcement and urged remaining ShinyHunters members to surrender, emphasizing that continued involvement will only lead to their eventual apprehension.