Pradipta eManuel
In a dramatic turn of events that has sent shockwaves through the cybersecurity world, Dutch authorities have apprehended Pepijn van der Stap, a 24-year-old convicted cybercriminal, on suspicion of aiding the notorious hacker group ShinyHunters. The arrest, which occurred on or around September 16th, has coincided with a significant escalation in ShinyHunters’ activities, including audacious data breaches targeting the FBI and even extortion attempts against the Russian ransomware collective Cl0p.
Van der Stap, hailing from Almere and Lelystad in the Netherlands, was no stranger to law enforcement. In 2023, he was convicted for his role in a series of data thefts and extortions that prosecutors estimated netted between €1.5 million and €2.7 million. During his trial, van der Stap adopted a dual persona, confessing to living a "Dr. Jekyll and Mr. Hyde existence." By night, he operated under the hacker handle "Umbreon," extorting victims and leaking their sensitive information on now-defunct English-language hacking forums like RaidForums and Breached. Paradoxically, by day, van der Stap was employed as a software engineer at Hadrian, an Amsterdam-based cybersecurity startup, and even volunteered at the Dutch Institute for Vulnerability Disclosure (DIVD), a non-profit security research group dedicated to identifying and reporting vulnerabilities.
His previous conviction resulted in a four-year prison sentence, with one year suspended. Van der Stap opted to remain in custody during his trial, citing ongoing psychological issues, including PTSD stemming from childhood trauma, for which he claimed he could not find adequate external treatment. He was released from prison in December 2025. In a September 9, 2026 interview with KrebsOnSecurity, van der Stap presented himself as a reformed individual striving to contribute positively to society. At the time of the interview, he was employed as the offensive security lead at Neo Security, a Dutch company that did not respond to requests for comment. He acknowledged ongoing civil lawsuits and restitution efforts for his past cybercrime victims, asserting his commitment to making amends. However, shortly after this interview, van der Stap abruptly ceased communication, and subsequent attempts by associates to reach him proved fruitless for two weeks.

Sources close to the investigation confirmed that Dutch authorities apprehended van der Stap and have been holding him for questioning. One source personally witnessed authorities removing items from his residence. The Dutch police have been actively seeking public assistance in identifying the voice of a ShinyHunters member who, in February 2026, used social engineering tactics to gain unauthorized access to Odido, the Netherlands’ largest mobile telecommunications provider. This intrusion, which involved tricking an Odido employee into logging into a spoofed website, resulted in the theft of data belonging to over 6.2 million Dutch citizens. ShinyHunters confirmed to Dutch media that the individual in the audio clip is indeed a member of their collective, stating their unwavering support for him, including emotional, mental, and financial assistance, and the provision of a criminal defense lawyer. The group also issued a scathing statement ridiculing the Dutch police as "a big joke," "incapable," "incompetent," "irrelevant," "unimportant," and "useless," vowing to carry out further large-scale data thefts in the Netherlands.
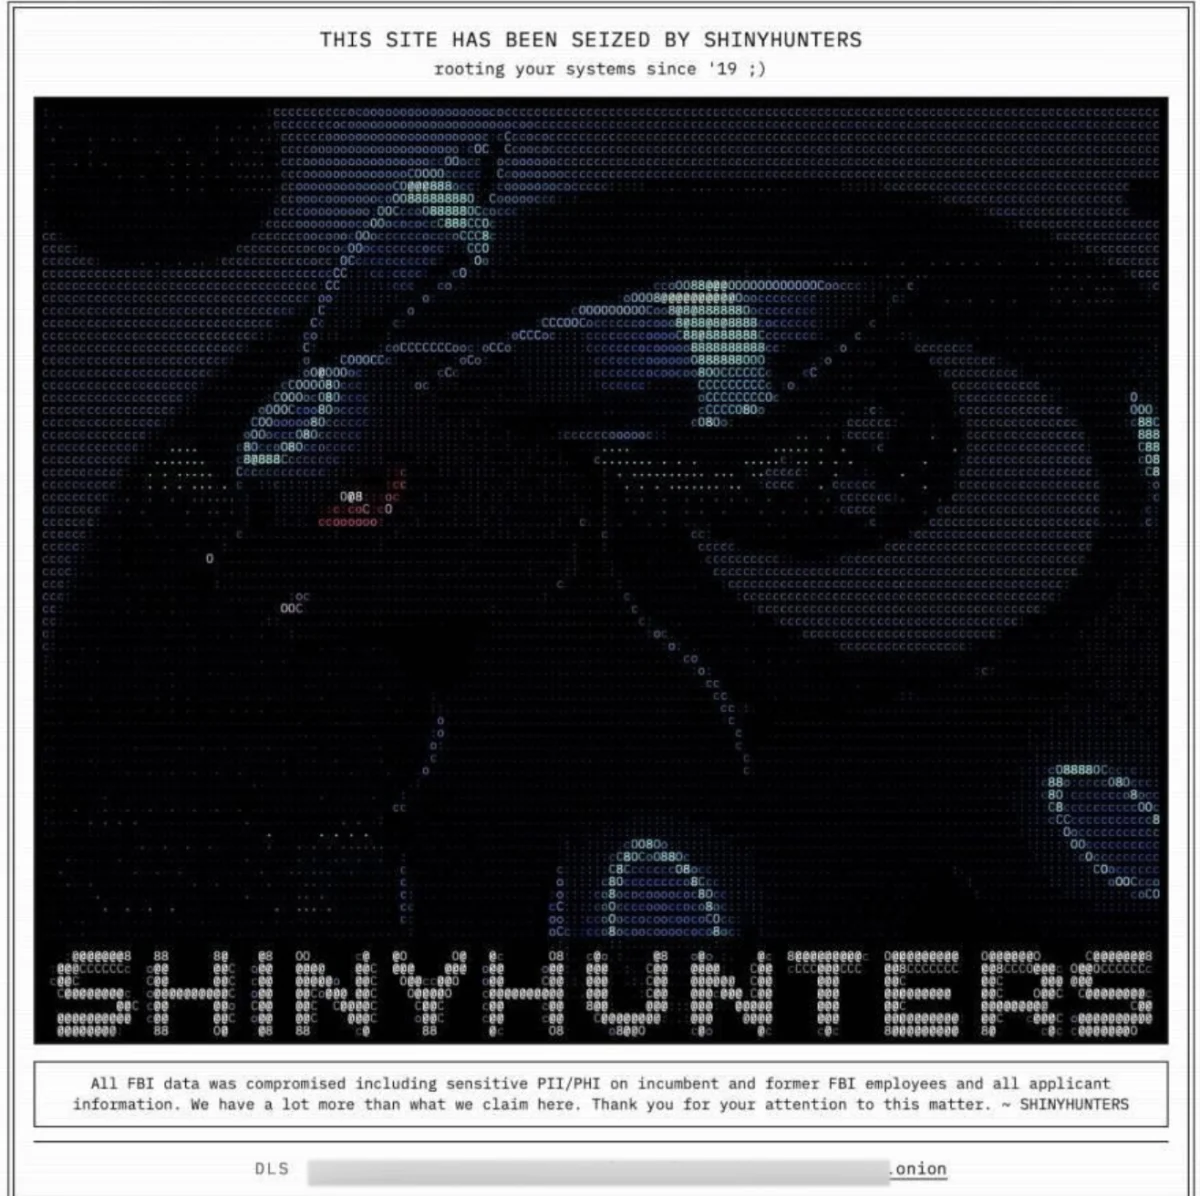
The timing of van der Stap’s arrest proved particularly volatile for ShinyHunters. In the immediate aftermath of his detention, the group launched a series of highly brazen and impactful attacks. They claimed responsibility for a significant breach of the FBI’s job application site, apply.fbijobs.gov, compromising sensitive information, including Social Security numbers, of over 5,000 officials. The stolen data reportedly included personal details, job titles, and even psychiatric and medical files of FBI personnel. The FBI acknowledged the breach, confirming the compromise of the portal.
ShinyHunters attributed their access to the FBI site and other victims to the exploitation of a recently patched vulnerability (CVE-2026-35273) in Oracle’s PeopleSoft, a widely used human resources software. While Oracle had issued a fix, ShinyHunters reportedly began exploiting it as a zero-day in June. Security firms like Mandiant offered mitigation strategies, including Web Application Firewall (WAF) rules, for organizations unable to apply the patch immediately. However, ShinyHunters employed a URL-encoding trick to bypass these WAF rules, enabling them to mass-exploit the vulnerability across numerous systems in various sectors, including higher education, technology, healthcare, agriculture, transportation, and government.
Significantly, the Umbreon alias, once associated with van der Stap, was conspicuously featured in ShinyHunters’ post-FBI hack propaganda. The defacement message left on the FBI jobs site included ASCII art of the Pokemon character Umbreon, a motif identical to one used in a 2020 hack of Hackforums. This reappearance has fueled speculation that the recent aggressive shift in ShinyHunters’ operations, characterized by high-profile attacks against the FBI and Cl0p, may be linked to a change in leadership.

Sources close to the ShinyHunters investigation suggest that the group has been taken over by a teenage cybercriminal from Amman, Jordan, known as "Rey," who operates as part of a larger cybercrime entity called ScatteredLapsussHunters (SLSH). SLSH is reportedly an amalgamation of three prominent hacking groups: Scattered Spider, LAPSUS$, and ShinyHunters. These sources indicate that Rey had an ongoing dispute with the Dutch hacker over control of the ShinyHunters brand and data, and that the prominent display of Umbreon in the FBI hack defacement was likely an attempt by Rey to frame the Dutchman.
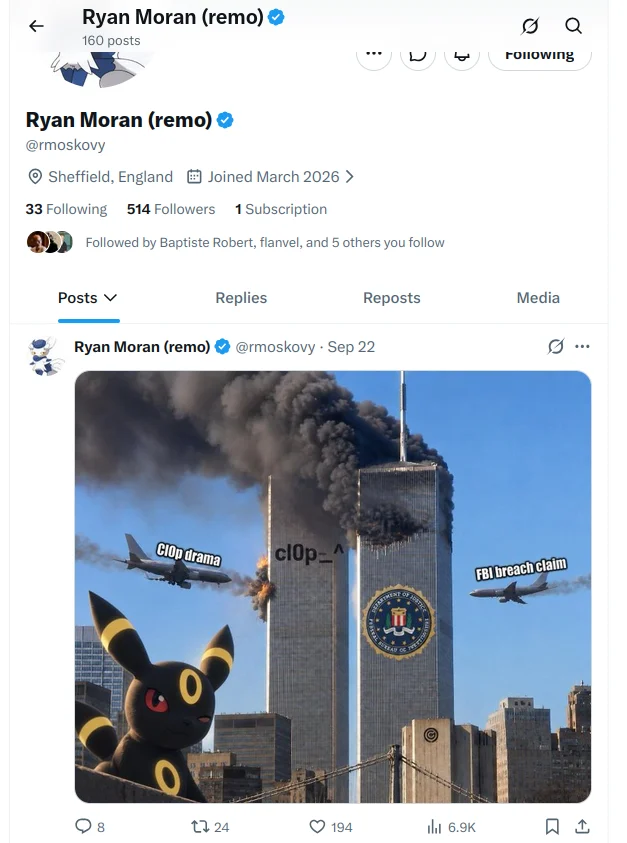
Rey was first identified by the cybersecurity firm KELA in March 2025. In an earlier profile of Rey by KrebsOnSecurity, Rey’s father, an employee of Royal Jordanian Airlines, forwarded interview requests to his son, who admitted to participating in ransomware attacks and expressed a desire to disengage from SLSH. Following the FBI jobs site hack, Rey’s Twitter/X account taunted the Cl0p ransomware group and the FBI with memes depicting them as the Twin Towers being struck by planes labeled "cl0p drama" and "fbi breach claim," with a giant Umbreon figure in the foreground. Shortly after KrebsOnSecurity contacted Rey’s father again for an interview regarding Rey’s alleged leadership of ShinyHunters, Rey deleted his Twitter/X account.
The animosity between SLSH and ShinyHunters appears to stem from a failed partnership earlier in the year. ShinyHunters and SLSH members had briefly collaborated with TeamPCP, a group specializing in compromising global code supply chains with malicious software. However, the partnership dissolved when ShinyHunters allegedly "went rogue," extorting victims using TeamPCP’s stolen credentials without sharing the profits. This betrayal occurred amidst efforts by Mandiant to infiltrate TeamPCP and invalidate stolen credentials by feeding them to cloud providers, leading to mutual blame among the cooperating hacker groups for the compromised data.
Mandiant researcher Austin Larsen noted that ShinyHunters had been enjoying a highly profitable extortion spree in 2026, on track to generate nearly $100 million. Van der Stap, however, has consistently claimed his motivation was not financial, but rather an obsession with building the world’s most comprehensive collection of stolen databases. He told Bloomberg in 2024 that hacking was "very easy" for him and not a compulsion, describing his habit as "collecting data, organizing data, downloading data, creating folders."

Meanwhile, DIVD, the nonprofit security research group where van der Stap previously volunteered, disclosed an internal cybersecurity incident last week, which appears to involve the malicious use of artificial intelligence. While DIVD has offered limited details, a spokesperson stated it does not seem related to ShinyHunters or the work of any former volunteers.
Further updates have emerged regarding the ongoing investigation. The Dutch police have confirmed the arrest of a 24-year-old in connection with the ShinyHunters investigation, stating the suspect will appear before the Rotterdam District Court on September 29th. In a startling development reported by RTL, investigators now suspect van der Stap of orchestrating at least two murders abroad. The FBI’s cyber division assistant director, Brett Leatherman, released a video message thanking Dutch law enforcement and urging remaining ShinyHunters members to surrender, warning that continued involvement would only lead to their discovery.