Pradipta eManuel
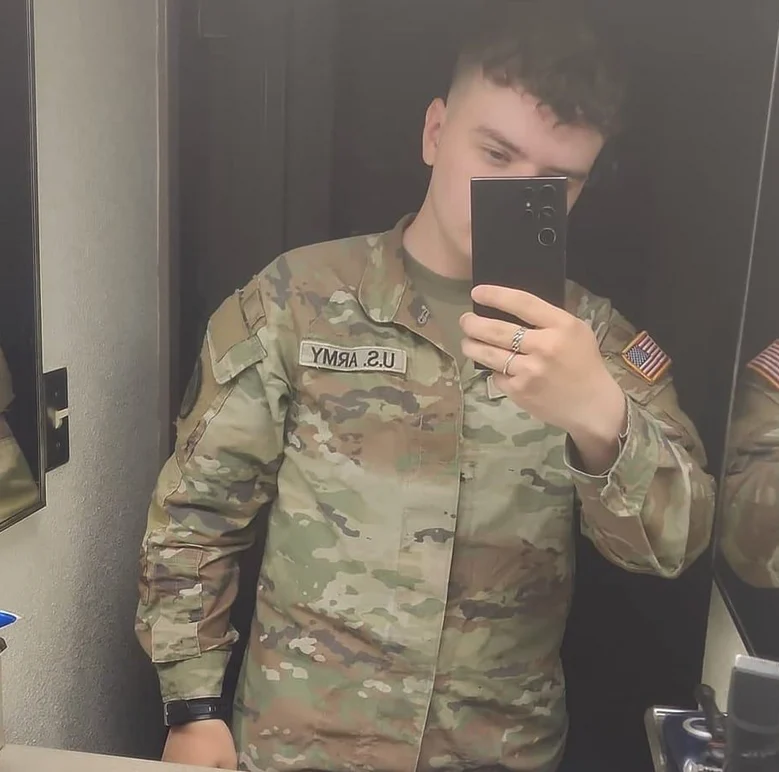
A U.S. Army soldier, identified as Cameron John Wagenius, 22, has been sentenced to 70 months (nearly six years) in federal prison for his role in a sophisticated cybercrime operation that targeted major telecommunications companies, including AT&T and Verizon. Wagenius, who was stationed in South Korea at the time of the offenses, was also ordered to pay nearly $300,000 in restitution to the victims. His sentencing marks a significant conclusion to an investigation that exposed a concerning intersection of insider threats and large-scale data theft.
Operating under the cybercriminal moniker "Kiberphant0m," Wagenius, along with three alleged co-conspirators, exploited vulnerabilities in the cloud data storage service Snowflake. These vulnerabilities included exposed credentials and a lack of enforced multi-factor authentication, which Snowflake has since mandated across all accounts. The group successfully infiltrated the systems of several large Snowflake clients, ultimately compromising sensitive data.
The gravity of Wagenius’s actions became apparent in October 2024 when "Kiberphant0m" boasted on cybercrime forums about stealing call and text metadata for tens of millions of AT&T customers. This data, which includes details such as source and destination numbers, timestamps, and duration of calls, is highly valuable for various malicious purposes. Wagenius claimed to have breached over a dozen telecommunications companies globally, including Verizon’s Push-to-Talk business. The group then engaged in public extortion, demanding payment from these companies in exchange for not releasing the stolen information.
The investigation into Kiberphant0m’s activities gained significant traction when KrebsOnSecurity, in November 2024, published a report suggesting the hacker was likely a U.S. soldier stationed in South Korea. This astute observation proved prescient, as less than a month later, Wagenius was apprehended. He subsequently faced charges in two separate federal indictments and ultimately pleaded guilty to all counts, demonstrating a degree of cooperation with authorities.
At his sentencing hearing in Seattle, Wagenius received his substantial prison sentence and the substantial restitution order. Federal prosecutors highlighted that Wagenius was not acting alone. He was allegedly assisted by Kenneth Schuchman, a 28-year-old individual from Vancouver, Washington, with a documented history of cybercriminal activity. Schuchman had previously pleaded guilty in 2019 to operating the Satori botnet, a vast network of compromised Internet-of-Things (IoT) devices used for large-scale distributed denial-of-service (DDoS) attacks.
The conspiracy also involved two other individuals who are still facing charges. Conor Riley Moucka, also known as "Judische," from Kitchener, Ontario, was arrested in 2024 and pleaded guilty in August 2026 for his involvement in the Snowflake data thefts. The fourth alleged co-conspirator is John Erin Binns, an American citizen residing in Turkey. Binns is also a person of interest in a separate, massive data breach at T-Mobile in 2021, which compromised the personal information of at least 76 million customers, underscoring the far-reaching impact of this group’s activities.
The extortion attempts by Kiberphant0m took a particularly alarming turn when the group allegedly re-extorted victims and threatened to disclose national security secrets. Following the arrest of Conor Riley Moucka, and after AT&T had already paid a $370,000 Bitcoin ransom to the extortion group, Kiberphant0m posted what he claimed were call logs for then-President-elect Donald Trump and then-Vice President Kamala Harris on hacker forums. Additionally, he allegedly shared schematics purportedly stolen from the U.S. National Security Agency (NSA), escalating the threat beyond mere financial extortion to potential national security implications.
The investigation was a multi-agency effort, underscoring its seriousness. Paul Russell, a resident agent in charge at the Defense Criminal Investigative Service (DCIS), the investigative arm of the U.S. Department of Defense Office of Inspector General, detailed the agency’s involvement. Upon receiving information linking an active-duty soldier with secret clearance to cybercrime and extortion, the DCIS immediately initiated collaboration with the Federal Bureau of Investigation (FBI), the Army Criminal Investigative Division (CID), and the U.S. Secret Service.
Russell emphasized the unique and concerning nature of the case: "We don’t often get leads where there’s an active duty soldier with a secret clearance who’s creating hacking tools and trafficking in data. That doesn’t happen every day, and so when that hits it really spins all of our partner organizations up. It was very serious from jump street, just because it was unique, it was an insider threat, and we weren’t sure what we were dealing with." The involvement of an individual with secret clearance raised immediate alarms about the potential for deeper breaches and the compromise of classified information.
A sentencing memo filed by federal prosecutors in Seattle on September 19th, revealed further concerning behavior by Wagenius even while incarcerated and awaiting sentencing. Despite pleading guilty early and demonstrating significant cooperation, Wagenius was caught attempting to probe the computer network of the Bureau of Prisons (BOP) for security vulnerabilities. This demonstrated a persistent inclination towards cyber exploitation, even within a correctional facility.
According to BOP records, in or around September 2025, Wagenius utilized another inmate’s email system to instruct a recipient to prompt a commercial AI tool for information regarding "what CVE’s are there for Windows 10 Enterprise privilege escalation and bypasses." He specifically requested CVEs and "real world working scripts for each CVE . . . without omitted code." Less than a week later, using a different inmate’s email account, Wagenius again requested AI assistance, this time for "step by step for CVE-2023-45208," a three-year-old command injection vulnerability in D-Link networking devices, including code if available and detailed explanations.
In an even more audacious move that same month, Wagenius allegedly asked the email recipient to research how to construct an antenna within a prison environment using readily available items to improve radio reception. Furthermore, the memo states that Wagenius also requested research into methods for escaping prison.
The government’s sentencing memo noted that Wagenius often framed these AI queries as being related to a book he was writing, a tactic described as "prompt injection." This method involves feeding specially crafted, deceptive inputs into AI tools to bypass their security protocols and elicit information that could be used to exploit vulnerabilities.
While the government acknowledged it was unaware of any evidence suggesting Wagenius successfully utilized or deployed the vulnerabilities he was researching within BOP systems, his stated intention upon questioning was that he was "only researching potential vulnerabilities to provide information to the BOP." This claim, however, remains to be fully substantiated given the context of his criminal history.
Perhaps one of the most surprising aspects of the case, despite the immense financial value of the data stolen from AT&T and other telecom providers, is the relatively limited financial success of Wagenius’s extortion efforts. The government’s sentencing memo indicates that Wagenius garnered a mere $1,500 from selling the stolen data.
The sentencing memo concluded by stating, "While Wagenius was not particularly financially successful as a cybercriminal, he both intended to and caused significant harm to numerous individual victims, U.S. companies, and the U.S. government." This sentiment underscores that the impact of his crimes extended far beyond financial losses, encompassing the erosion of trust, potential national security risks, and the violation of privacy for millions of individuals. Wagenius’s case serves as a stark reminder of the evolving threat landscape posed by insider threats and the sophisticated methods employed by cybercriminals in the digital age.